
Many organizations purchase VAPT as a single service without understanding that Vulnerability Assessment (VA) and Penetration Testing (PT) are two distinct cybersecurity exercises with different objectives, methodologies, deliverables, costs, and regulatory considerations.
Understanding these differences helps organizations make informed decisions, avoid overspending on unnecessary assessments, and ensure they receive meaningful security assurance rather than merely a compliance report.
VAPT Is Not One Exercise
One of the most common misconceptions is that VAPT is a single cybersecurity activity.
In reality, VAPT consists of two separate security exercises:
- Vulnerability Assessment (VA)
- Penetration Testing (PT)
Although they are often sold together, they answer different cybersecurity questions and deliver different outcomes.
Vulnerability Assessment (VA)
A Vulnerability Assessment is designed to identify known security weaknesses within systems, applications, cloud environments, servers, network devices, and security appliances.
The primary objective is to answer:
“What known vulnerabilities exist in my environment?”
-
- Missing security patches
- Unsupported software versions
- Weak encryption settings
- Security misconfigurations
- Exposed services
- Known CVE vulnerabilities
- Weak security baselines
A VA is typically broad in scope and relies heavily on security scanning tools and vulnerability databases.
Penetration Testing (PT)
A Penetration Test focuses on determining whether vulnerabilities can be exploited and what impact an attacker could achieve.
The primary objective is to answer:
“Can an attacker compromise my system, and what damage could result?”
A PT typically evaluates:
- Exploitable vulnerabilities
- Authentication weaknesses
- Access control issues
- Privilege escalation paths
- Business logic flaws
- Application security weaknesses
- Real-world attack scenarios
Unlike Vulnerability Assessments, Penetration Tests contain a significant manual component and require experienced security professionals to validate findings and assess business impact.
Vulnerability Assessment vs Penetration Testing
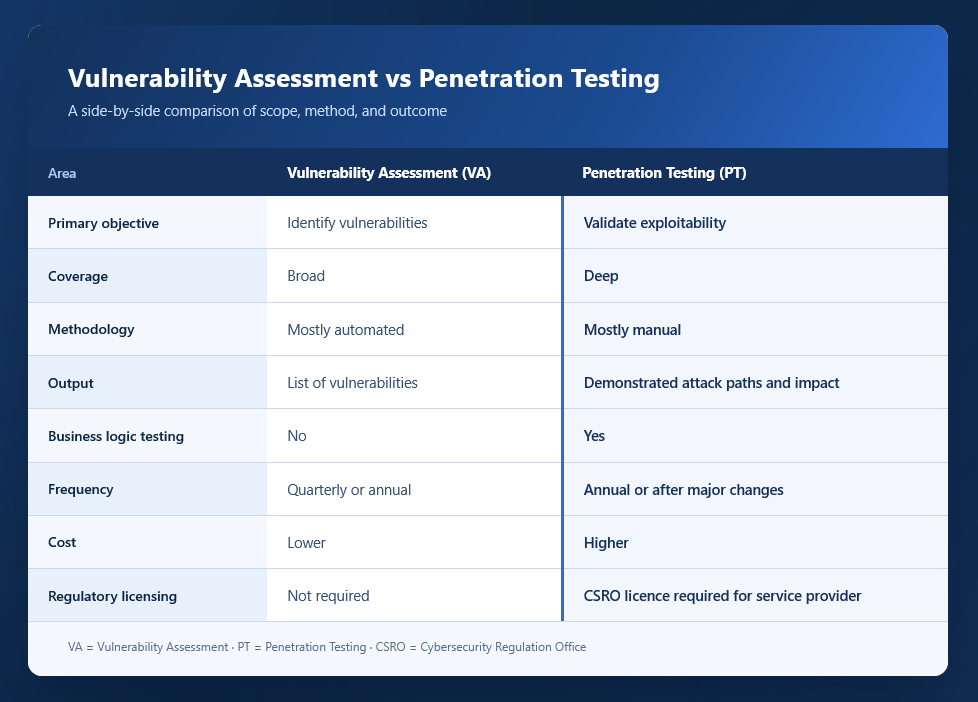
The frequencies above reflect common practice, not a legal requirement. The exception is Critical Information Infrastructure, where the Cybersecurity Code of Practice sets Vulnerability Assessment and Penetration Testing at least every 12 months for IT systems and every 24 months for OT systems.
Who Can Perform a Vulnerability Assessment?
A Vulnerability Assessment may be performed by:
- Internal IT teams
- Cybersecurity consultants
- Managed Service Providers (MSPs)
- Managed Security Service Providers (MSSPs)
- Security analysts using approved assessment tools
Many organizations incorporate Vulnerability Assessments into their ongoing cybersecurity and vulnerability management programs.
Because the assessment focuses on identifying vulnerabilities rather than exploiting them, Vulnerability Assessment services are generally not regulated under Singapore’s cybersecurity licensing framework.
To be precise, the Cybersecurity Act licenses only two services. One of them is penetration testing (PT). The other is managed security operations center (SOC) monitoring. Vulnerability Assessment on its own is not licensable, which is why your own IT team or an MSP can run one without holding anything.
Who Can Perform a Penetration Test?
Penetration Testing is regulated under Singapore’s Cybersecurity Act.
Organizations engaging a Penetration Testing provider should verify that the provider holds a valid Penetration Testing Service License issued by the Cyber Security Services Regulation Office (CSRO).
Before engaging a provider, organizations should consider requesting:
- CSRO license details
- Testing methodology
- Scope definition
- Sample reports
- Retesting arrangements
- Qualifications of assigned consultants
Licensed providers can be verified through the CSRO public register:
Cyber Security Services Regulation Office (CSRO)
View CSRO Public Register
A reputable provider should clearly define the testing scope, assumptions, methodology, exclusions, reporting framework, and retesting process before commencement of the engagement.
What Affects the Cost of VAPT?
The cost of a Vulnerability Assessment or Penetration Test is influenced by many factors, including the scope of systems being tested, the complexity of the environment, the testing methodology selected, and the level of assurance required.
Scope and Complexity
The number and type of assets being assessed are often the largest contributors to cost.
-
- Websites
- Business applications
- Mobile applications
- APIs
- Servers
- Firewalls
- Cloud environments
- Active Directory environments
- Internal networks
A security assessment for a single corporate website will naturally require less effort than an assessment involving multiple applications, cloud platforms, APIs, and internal infrastructure.
Internal and External Testing
Security assessments may focus on:
External Testing
Assessment of Internet-facing systems such as:
- Websites
- Firewalls
- VPN gateways
- Public APIs
- Remote access services
Internal Testing
Assessment of internal systems including:
- Active Directory
- Internal applications
- Servers
- Workstations
- Privileged access controls
Where both internal and external assessments are required, the overall effort typically increases.
Black Box, Grey Box and White Box Testing
The selected testing methodology can significantly influence both effort and cost.
Black Box Testing
The tester is provided with little or no information beforehand and approaches the environment from the perspective of an external attacker.
Grey Box Testing
The tester is provided with limited information or standard user credentials before the assessment begins.
This is one of the most common approaches used for web applications and business systems.
White Box Testing
The tester is provided with extensive information regarding the target environment, such as:
- Network architecture diagrams
- System documentation
- Source code
- Administrative credentials
- Security design documentation
White Box assessments are typically used where organizations require comprehensive validation of applications, systems, or security controls.
Production and After-Hours Testing
- Maintenance windows
- Weekends
- Public holidays
- After-office hours
This is particularly common within healthcare, financial services, manufacturing, and customer-facing production environments where service disruptions must be minimized.
The additional planning and coordination required may increase overall project costs.
What Is the Cost of VAPT?
One of the most common questions raised by business owners and IT managers is:
“How much should we budget for a Vulnerability Assessment and Penetration Test?”
-
- One public-facing website
- One firewall protected by a single Internet-facing WAN IP address
- Black Box / Authenticated Web Application and Network VAPT
- Office-hours testing
The quotations received varied significantly:
| Provider | Quoted Price |
|---|---|
| Provider A | S$2,500 |
| Provider B | S$6,000 |
| Provider C | S$13,200 |
All proposals included the assessment and technical report.
About this comparison. Quotes were obtained in August 2026 for the scope above and are shown anonymously. They are indicative, not offers, and three data points are not a market rate.
The results show that pricing can vary substantially even when the scope appears similar. Organizations often pay for different levels of testing effort, methodology, consultant experience, quality assurance, reporting detail, remediation guidance, retesting services, and overall assurance.
Service provider for government, enterprise, mid-size, and SMEs.
One important lesson from our research was that not all VAPT providers serve the same market.
During discussions with various PT Service providers, we learned that some firms primarily serve government agencies, Critical Information Infrastructure (CII) operators, financial institutions, and large enterprises. In one discussion, we were surprised to learn that the provider’s typical engagement size exceeded S$1 million. Their services were designed for complex enterprise environments rather than SMEs.
This highlighted an important lesson:
The objective is not to find the biggest VAPT provider. The objective is to find the right provider based on your organization’s size, regulatory requirements, risk profile, and budget.
For SMEs, charities, non-profit organizations, clinics, and professional services firms, the most suitable provider may differ markedly from that engaged by banks, healthcare clusters, government agencies, or Critical Information Infrastructure operators.
An Important Cost Consideration: Remediation Is Usually Not Included
One of the biggest surprises for organizations engaging a VAPT provider for the first time is that the engagement often concludes with the delivery of the report.
The assessment identifies vulnerabilities, weaknesses, and security findings. However, the remediation work required to fix those findings is typically not included in the assessment fee.
Examples of remediation work include:
- Applying security patches
- Firewall reconfiguration
- Microsoft 365 hardening
- Cloud security hardening
- Fixing application vulnerabilities
- Operating system upgrades
- Implementation of additional security controls
These activities are usually treated as separate implementation projects.
Organizations should therefore budget not only for the assessment itself, but also for the resources required to remediate the findings afterward.
A Vulnerability Assessment or Penetration Test improves security only when the findings are reviewed, prioritized, and addressed appropriately.
How Often Should VAPT Be Performed?
Frequency should follow risk and obligation, not the calendar.
CII owners: every 12 months for IT systems under the Code of Practice. Financial institutions: annual testing of internet-facing systems is the industry benchmark, per the ABS Penetration Testing Guidelines 2.0.
Annual: an annual Vulnerability Assessment on critical and internet-facing systems, and a Penetration Test on public-facing applications handling sensitive or personal data.
Major Changes: Events matter more than anniversaries. A major release, a cloud migration, an acquisition, or a new customer portal is a better trigger than the date of the last report.
Recommendation
For most SMEs, charities, and non-profit organizations, a Vulnerability Assessment should be viewed as an ongoing cybersecurity practice rather than a one-time compliance exercise.
The objective should not be to obtain the cheapest report. The objective should be to obtain meaningful security assurance, actionable recommendations, and practical guidance that help reduce cyber risks and improve organizational resilience.
For organizations considering a Vulnerability Assessment or Penetration Test, Entrust Network can assist with scope definition, vendor selection, proposal review, remediation planning, and independent cybersecurity advisory to help ensure the assessment delivers practical business value.
Continue Reading
Previously in Part 1: Is VAPT Mandatory in Singapore? What SMEs Need to Know About Cybersecurity Compliance
Coming in Part 3: From Vulnerability Scanners to AI-Powered Exposure Management
Frequently Asked Questions
Often not. If the goal is to find and fix known weaknesses across a broad estate, a Vulnerability Assessment is the right tool and the better value. A Penetration Test answers whether someone could actually get in and, if so, how far. We see plenty of SMEs buy a bundled VAPT when a VA plus a scoped application test would have served them better.
Not always, but the difference is effort, not goodwill. Ask how many consultant-days are allocated, who does the work, whether findings are manually validated to strip false positives, and whether the report includes prioritized remediation. That explains most price gaps.
Scope and its limitations stated plainly, confirmed findings separated from unconfirmed ones, business impact rather than only CVSS scores, and remediation steps specific enough for your IT team or vendor to act on. An executive summary a non-technical director can read is a good sign. An exported scanner list is not.
They can, but consider the conflict of interest. A vendor assessing its own configuration work has an incentive, even an unconscious one, not to find much. For higher-risk systems, independent testing gives more meaningful assurance.
Agree on it before the engagement starts. Exclude test types, the testing window, named emergency contacts on both sides, and a stop condition. Denial-of-service testing, in particular, should be in or out of scope in writing.
Author
Zou Yu Heng
Cybersecurity and Digital Forensics Practitioner
Zou Yu Heng is a cybersecurity and digital forensics practitioner specializing in vulnerability assessment, security testing, and risk management. He has experience conducting website and business application security assessments, security risk evaluations, and security control validation. As a member of the ISO/IEC 27001 ISMS and SS 714 DPTM implementation team, Yu Heng supports incident response planning, penetration testing, and cybersecurity compliance initiatives. He holds a Diploma in Cybersecurity from Singapore Polytechnic.
Technical Review and Contributing Author
Jamson Lim
IT Director, Data Protection Officer (DPO) and Cybersecurity Consultant
Jamson Lim is an IT and cybersecurity professional with over 20 years of experience in cloud security, data protection, secure infrastructure, and compliance advisory. He holds a Master of Computing from the National University of Singapore (NUS) and an Advanced Diploma in Data Protection from Singapore Management University (SMU), and is certified as a Certified Ethical Hacker (CEH) and Certified Linux Systems Engineer (CLSE). Jamson advises SMEs, non-profit organizations, and charities on cybersecurity, data protection, ISO/IEC 27001, PDPA, MAS TRM, and healthcare security compliance.
