
One of the most common cybersecurity questions raised by business owners, management teams and IT managers is:
Is VAPT mandatory in Singapore?
The answer depends on the organization’s industry sector, regulatory obligations, data sensitivity, contractual requirements, cyber insurance requirements and overall cybersecurity risk profile. For some organizations, security testing may be mandatory. For many others, it is an expected or recommended practice that supports cyber resilience, regulatory compliance and risk management.
Understanding when and why security testing is required is often more important than determining whether VAPT is mandatory.
Why There Is So Much Confusion About VAPT
A common misconception is that VAPT is a single annual compliance exercise that every organisation must perform.
In practice, different organizations face different cybersecurity risks and regulatory obligations. The security testing requirements for a healthcare provider, financial institution, charity, educational institution or professional services firm can vary significantly.
-
- What systems they operate
- What information they are responsible for protecting
- What regulatory requirements apply
- What would happen if those systems were compromised
Cybersecurity testing should always be driven by risk, not by marketing claims or compliance myths.
When Is Security Testing Mandatory, Expected, Recommended or Contractual?
Cybersecurity testing requirements generally fall into four categories:
| Category | Description |
|---|---|
| Mandatory | Required by legislation or regulatory frameworks |
| Expected | Considered a reasonable security practice by regulators |
| Recommended | Based on cybersecurity risk management principles |
| Contractual | Required by customers, tenders, insurers or business partners |
Many organizations fall into more than one category.
For example, a healthcare organization may be expected to implement security testing because of healthcare cybersecurity guidelines, while also being contractually required to perform security assessments by customers or cyber insurers.
Critical Information Infrastructure (CII) and CSA Requirements
Some organizations are subject to specific cybersecurity obligations under Singapore’s Cybersecurity Act.
The Cyber Security Agency (CSA) requires designated Critical Information Infrastructure (CII) owners to conduct regular cybersecurity assessments, including Vulnerability Assessments and Penetration Testing. These obligations apply to systems formally designated by CSA as critical to Singapore’s national security, economy, public health or public safety.
A common misunderstanding is that all organisations operating in healthcare, finance, transport, telecommunications or government sectors are automatically classified as Critical Information Infrastructure.
This is not the case.
An organization becomes subject to CII obligations only after receiving formal designation from CSA. Most SMEs, charities, clinics, schools and private businesses are not designated CII owners.
PDPA and Reasonable Security Arrangements
The Personal Data Protection Act (PDPA) does not prescribe annual VAPT requirements.
However, organizations must implement reasonable security measures to protect personal data. This includes adopting appropriate security measures based on the volume, sensitivity and risk associated with the personal data being processed.
For organizations that handle customer information, donor information, health records, employee records or financial information, regular security reviews and vulnerability management practices may help demonstrate accountability and due diligence.
MAS Technology Risk Management (TRM)
Organizations operating within the financial services sector are subject to heightened cybersecurity expectations.
The Monetary Authority of Singapore (MAS) expects financial institutions to implement security testing and vulnerability management practices appropriate to the technology and cyber risks they face. This typically includes regular Vulnerability Assessments, security reviews, security testing, and where appropriate, Penetration Testing of critical systems and applications.
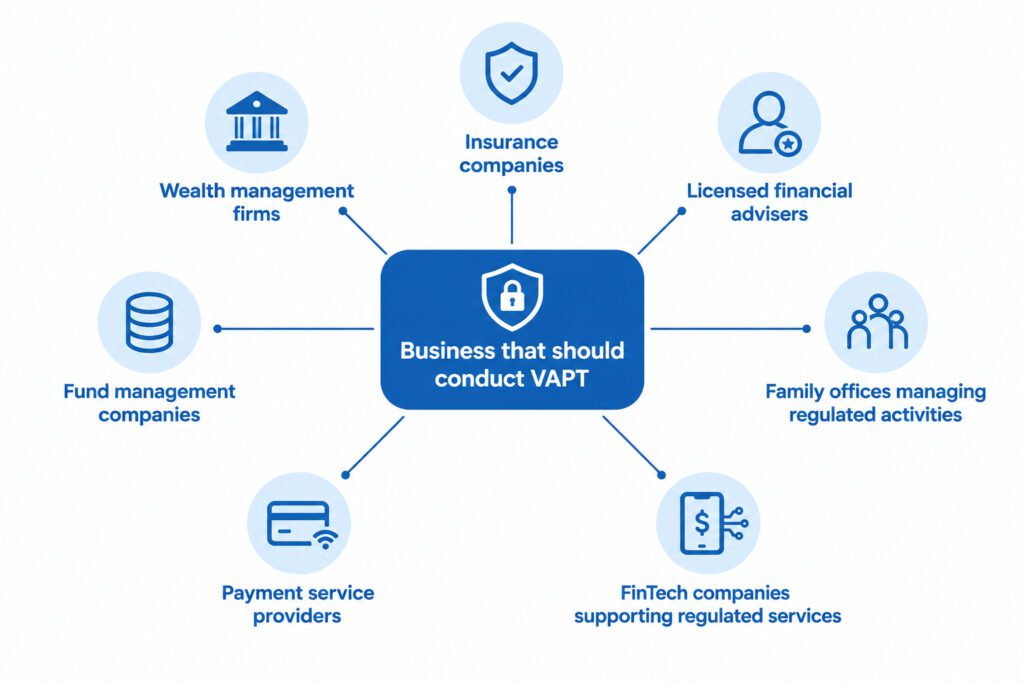
Examples include:
- Insurance companies
- Wealth management firms
- Licensed financial advisers
- Fund management companies
- Family offices managing regulated activities
- Payment service providers
- FinTech companies supporting regulated services
While MAS does not prescribe a single VAPT frequency applicable to all organizations, regulated financial institutions are generally expected to conduct periodic security assessments as part of their Technology Risk Management program and overall cyber resilience strategy.
For most organizations operating customer-facing portals, financial applications, online transaction platforms, payment systems, or internet-facing business applications, regular Vulnerability Assessments and periodic Penetration Testing should be considered standard cybersecurity practices rather than optional exercises.
MOH Healthcare Cybersecurity and Data Security Essentials
Healthcare organizations manage highly sensitive personal and medical information.
The healthcare sector is increasingly subject to cybersecurity and data protection expectations through various healthcare cybersecurity initiatives and frameworks. Organizations handling patient records should assess security risks regularly and implement controls appropriate to the systems and data they manage.
It is important to note that a small GP clinic, dental clinic or specialist practice is not automatically classified as Critical Information Infrastructure.
Security testing requirements should be assessed based on business risk, patient data sensitivity and applicable healthcare requirements.
Which Businesses May Not Require Regular Penetration Testing?
Not every organization requires annual penetration testing.
Examples may include:
- Professional services firms
- Marketing agencies
- Interior design firms
- Small accounting practices
- Small charities and non-profit organisations
Where an organization does not operate public-facing applications, online payment systems or high-risk business applications, regular security reviews, vulnerability management, patching, access control reviews and Multi-Factor Authentication (MFA) may provide an appropriate cybersecurity baseline.
When Should a Business Consider Penetration Testing?
Penetration testing becomes increasingly important when an organization operates:
- Customer portals
- E-commerce platforms
- Internet-facing applications
- Public APIs
- Mobile applications
- Healthcare systems
- Financial systems
- Online payment services
- Custom-developed applications
These systems are more exposed to cyberattacks and may contain business-logic weaknesses, authentication errors, and authorization flaws that automated security scanning cannot detect.
When a system compromise could result in significant business disruption, financial loss, regulatory exposure, or data breaches, penetration testing should be seriously considered.
Frequently Asked Questions
If your organization has been designated as operating Critical Information Infrastructure (CII), CSA will formally notify the organization and specify the applicable obligations. Most SMEs, charities and private organizations are not designated CII owners.
Not necessarily. Security testing requirements depend on the systems being operated, the sensitivity of patient information and applicable healthcare cybersecurity obligations. Most private clinics are not designated as CII owners.
Financial institutions are generally expected to conduct security testing as part of their Technology Risk Management program. The required scope and frequency depend on the organization's regulatory and risk requirements.
No. ISO 27001 requires organizations to implement vulnerability management and security testing appropriate to their risk environment. It does not prescribe annual VAPT.
There is no blanket legal requirement. However, charities and non-profit organizations that process personal data remain subject to the PDPA and should implement appropriate security controls based on their risk profile.
In most situations, responsibility is shared.
The provider is generally responsible for securing the infrastructure and application platform.
The organization remains responsible for user access management, security configuration, data governance, compliance obligations, and protection of personal data.
Outsourcing a system does not automatically transfer accountability for data protection and cybersecurity responsibilities.
Our recommendation for SMEs, Charities and Non-Profit Organisations
Whether VAPT is required in Singapore depends on the organization’s regulatory obligations, industry sector, data sensitivity, contractual commitments, and overall cybersecurity risk profile.
For some organizations, cybersecurity testing may be mandatory. For many SMEs, charities, and nonprofit organizations, it is a recommended practice that helps demonstrate reasonable security arrangements, cyber resilience, and good governance.
-
- Conduct regular cybersecurity and security configuration reviews.
- Perform annual Vulnerability Assessments on critical business systems and internet-facing services.
- Conduct annual Penetration Testing for public-facing applications that process significant volumes of sensitive or personal data.
- Review third-party vendors and cloud service providers regularly.
- Implement Multi-Factor Authentication, access reviews, backup testing and vulnerability management processes.
Final Verdict for SMEs, Charities and Non-Profit Organizations
For most SMEs, charities and non-profit organizations in Singapore, Vulnerability Assessment and Penetration Testing (VAPT) is generally not a mandatory regulatory requirement.
However, VAPT should be viewed as a recommended, ongoing cybersecurity practice rather than a one-time compliance exercise.
Coming in Part 3: From Vulnerability Scanners to AI-Powered Exposure Management
Author
Zou Yu Heng
Cybersecurity and Digital Forensics Practitioner
Zou Yu Heng is a cybersecurity and digital forensics practitioner specializing in vulnerability assessment, security testing, and risk management. He has experience conducting website and business application security assessments, security risk evaluations, and security control validation. As a member of the ISO/IEC 27001 ISMS and SS 714 DPTM implementation team, Yu Heng supports incident response planning, penetration testing, and cybersecurity compliance initiatives. He holds a Diploma in Cybersecurity from Singapore Polytechnic.
Technical Review and Contributing Author
Jamson Lim
IT Director, Data Protection Officer (DPO) and Cybersecurity Consultant
Jamson Lim is an IT and cybersecurity professional with over 20 years of experience in cloud security, data protection, secure infrastructure, and compliance advisory. He holds a Master of Computing from the National University of Singapore (NUS) and an Advanced Diploma in Data Protection from Singapore Management University (SMU), and is certified as a Certified Ethical Hacker (CEH) and Certified Linux Systems Engineer (CLSE). Jamson advises SMEs, non-profit organizations, and charities on cybersecurity, data protection, ISO/IEC 27001, PDPA, MAS TRM, and healthcare security compliance.
