
Quick summary: Sophos Fusion combines Sophos and Secureworks capabilities to strengthen EDR, XDR, MDR, threat intelligence, AI-assisted investigation, automation, email monitoring, and next-generation SIEM. |
The Biggest Upgrade to Sophos Security
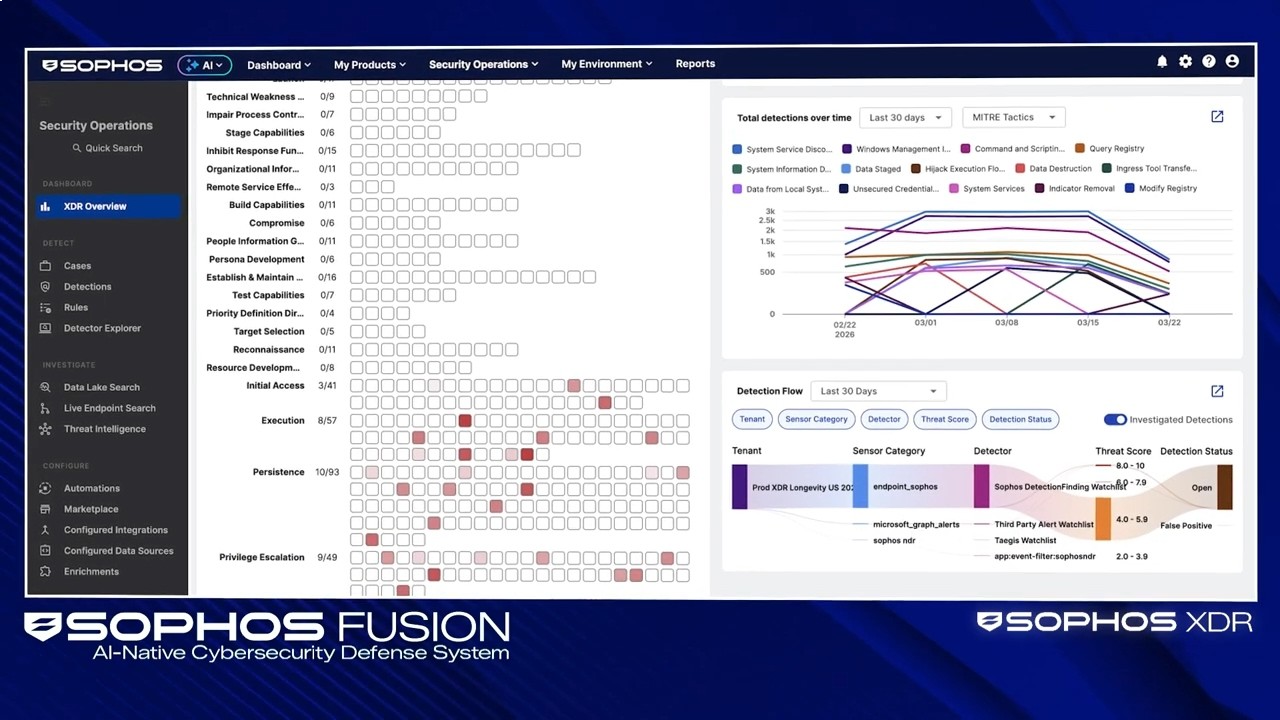
Sophos is rolling out Sophos Fusion, its AI-Native Cybersecurity Defense System, with major enhancements to Sophos EDR, Sophos XDR, and Sophos MDR. The phased upgrade program began in August 2026 and introduces a redesigned security operations experience, broader detection capabilities, new integrations, automation, and AI-assisted workflows.
Sophos Acquired SecureWorks
In 2025, Sophos acquired Secureworks, a provider of managed detection and response, threat intelligence, and the Taegis XDR platform. The acquisition strengthens Sophos’s capabilities in threat detection, threat hunting, security operations, and AI-driven cybersecurity, forming the foundation of Sophos Fusion.
What is Sophos Fusion?
Sophos Fusion is the architecture behind the expanded security operations portfolio. It combines artificial intelligence, threat intelligence, detection engineering, threat hunting, investigation, and automated response in a unified ecosystem.
| Before Fusion | With Sophos Fusion |
|---|---|
| Endpoint-focused security | Broader security operations platform |
| Separate product workflows | Integrated analyst experience |
| Primarily manual investigation | AI-assisted investigation and search |
| Limited automation | SOAR connectors, playbooks, and response actions |
| Endpoint-centred visibility | Cross-platform telemetry and integrations |
What’s New in Sophos EDR, XDR and MDR with Fusion and AI?
| Capability | Sophos EDR | Sophos XDR Powered by Sourceworks | Sophos MDR |
|---|---|---|---|
| Security Operations interface | Replaces Threat Analysis Center | Replaces Threat Analysis Center | Used by Sophos analysts |
| AI-assisted investigation | Included | Included | Included |
| Natural language search | Included | Included | Included |
| Endpoint Data Lake search | Enhanced | Enhanced | Used for managed investigations |
| Saved queries and query builder | Included | Included | Analyst operated |
| Threat hunting | Customer managed | Customer managed | Continuous, intelligence-led service |
| Bulk device isolation and response | Included | Included | Included |
| Tamper and anti-exploitation protection | Enhanced | Enhanced | Enhanced |
| AI Detection Analysis | Not available | Included | Included |
| Secureworks detections | Not available | Thousands of additional detectors | Used by MDR service |
| Third-party integrations | Limited | Expanded, with two-way actions | Expanded, with managed response |
| Identity and Microsoft 365 response | Not available | Included where supported | Included where supported |
| Email Monitoring System | Not available | Included | Included |
| Security automation (SOAR) | Not available | Included | Used by MDR operations |
| Agentic AI threat hunting | Not available | Not listed as a customer-led service | Included with analyst review |
| 24x7 human monitoring and response | Customer responsibility | Customer responsibility | Included |
| Next-Gen SIEM | Not available | Optional add-on | Optional add-on |
Four Enhancements Worth Reviewing
1. Security Operations replaces Threat Analysis Center
The redesigned experience brings alerts, context, investigation workflows, threat hunting, and response actions into a more unified analyst workspace.
2. AI-assisted investigation and threat hunting
Natural language search, guided query building, AI Detection Analysis, and improved Data Lake search are intended to reduce investigation time and make threat hunting more accessible.
3. Sophos Email Monitoring System
EMS provides vendor-agnostic email threat monitoring alongside an existing email security solution. It is included with Sophos XDR and Sophos MDR and can add visibility for Microsoft 365 environments.
4. Next-Gen SIEM
The optional add-on extends telemetry retention, supports compliance-oriented use cases, and allows additional data integrations. This brings Sophos into closer competition with established SIEM and security operations platforms.
What This Means for Existing Customers
| Customer | Primary gain |
|---|---|
| Sophos EDR | Faster endpoint investigation, natural language search, stronger hunting workflows, and bulk response actions |
| Sophos XDR | Additional Secureworks detections, AI analysis, expanded integrations, EMS, SOAR, and optional SIEM |
| Sophos MDR | Continuous intelligence-led hunting, agentic AI support, expanded two-way response, EMS, and 24x7 analyst operations |
| Microsoft 365 environments | Email monitoring and supported identity or Microsoft 365 response actions |
| MSPs and internal SOC teams | More consolidated workflows, automation, integrations, and investigation context |
Our Review
Sophos Fusion is more than a user-interface refresh. It marks a strategic shift from endpoint-centered protection to a broader security operations platform that combines prevention, detection, investigation, automation, threat intelligence, and managed response.
The largest functional gains appear in Sophos XDR and MDR. XDR offers broader detection, integrations, AI analysis, and SOAR capabilities, while MDR adds continuous intelligence-led hunting and expert-led 24×7 operations.
EDR customers still benefit from a more efficient investigation experience and stronger endpoint response workflows.
Important rollout note: The upgrade is being deployed in phases. Features, timing, integrations, and entitlements may vary by licence and tenant. Customers should verify availability in Sophos Central and current official documentation. |
Official References
Brina Teo is a cybersecurity practitioner specializing in Security Information and Event Management (SIEM), endpoint security, and Microsoft 365 security assessments. Her expertise includes Wazuh SIEM deployment, security monitoring, threat detection, incident investigation, and Sophos Endpoint Security administration. Brina holds a Diploma in Cybersecurity and Digital Forensics from Temasek Polytechnic and is passionate about security operations, cloud security, and cyber threat management.
Jamson Lim is an IT and cybersecurity professional with over 20 years of experience in cloud security, data protection, secure infrastructure, and compliance advisory. He holds a Master of Computing from the National University of Singapore (NUS) and an Advanced Diploma in Data Protection from Singapore Management University (SMU), and is certified as a Certified Ethical Hacker (CEH) and Certified Linux Systems Engineer (CLSE). Jamson advises SMEs, non-profit organizations, and charities on cybersecurity, data protection, ISO/IEC 27001, PDPA, MAS TRM, and healthcare security compliance.
